PCI DSS v4.0.1 Merchant Software
- Simplify your PCI DSS program by removing unnecessary complexity.
- Accurate scoping is achieved and maintained.
- Optimizes subrequirement task completion through automated task delegation and assignment.
- Never miss a scheduled activity.
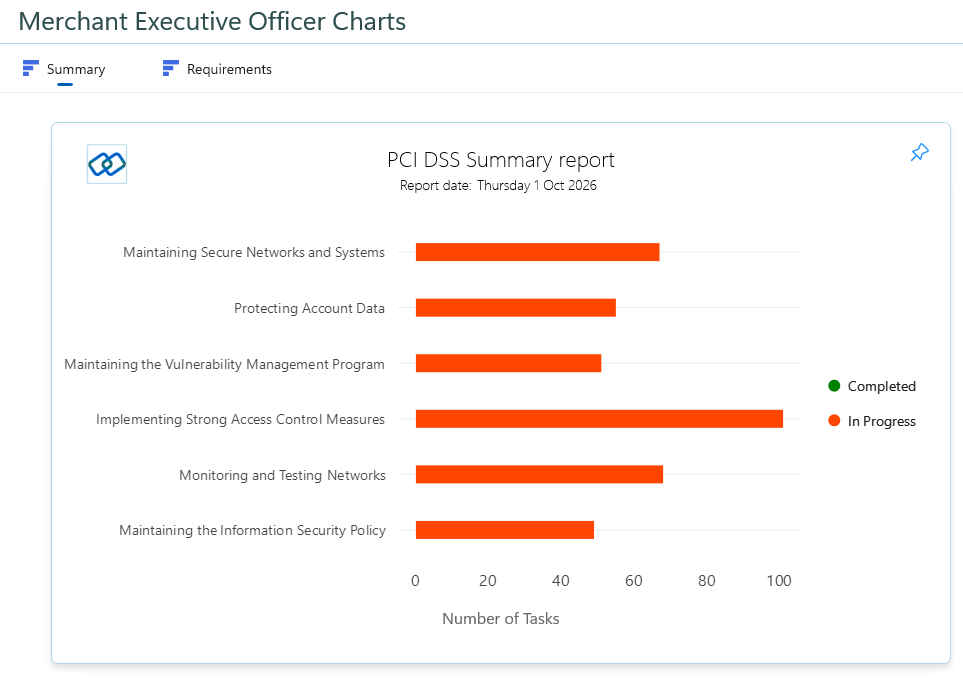
- Real time charts and reports track operational progress, giving reassurance to all stakeholders.
- Maintains an accurate PCI DSS indexed evidence library.
- Saves cost, time and resources by autocompleting your SAQ and AOC into the official PCI SSC attestation templates.
PCI Linx is built for PCI DSS challenges
PCI DSS environments are rarely simple. Scope is spread across teams, technologies, service providers, regions, facilities and locations, making it hard to maintain a clear and reliable picture across the year; PCI Linx is designed for this reality.
PCI Linx is built around comprehensive inventories, structured tasks and PCI leadership, so that your PCI DSS program is managed for audits in a defined and repeatable way.
PCI Linx addresses the shortfalls of GRC solutions and fully supports PCI DSS operational practices.
SAQ Eligibility
Accurate PCI DSS Scoping
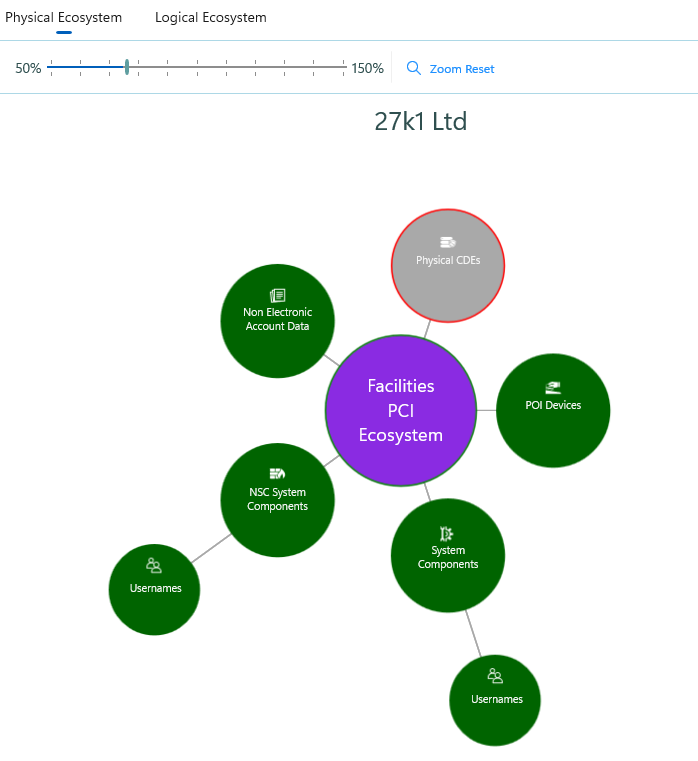
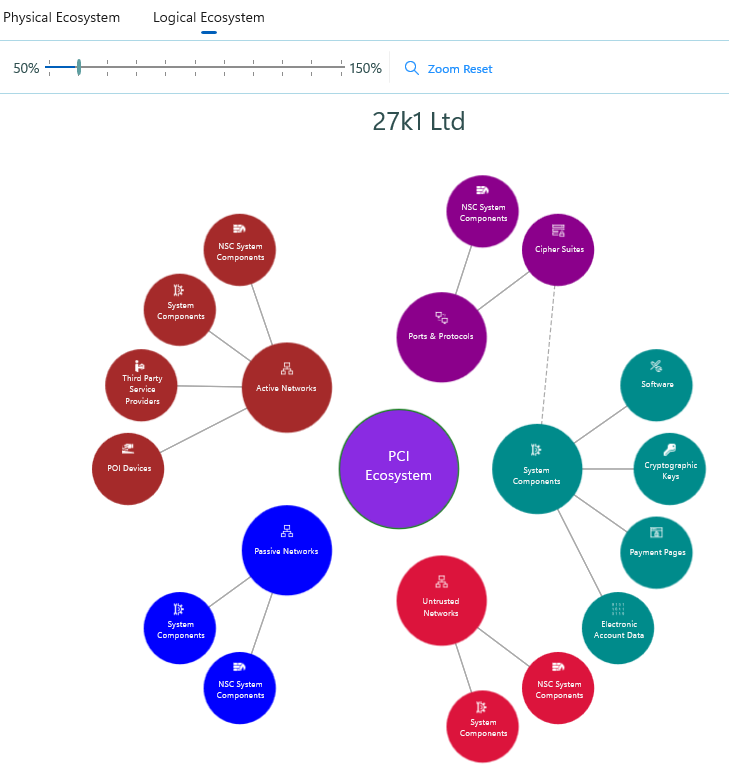
PCI DSS Ecosystem
PCI Linx provides a visual representation enabling you to clearly identify any errors in your PCI DSS scope.
Inventory Control
Tasks & Job Roles
Operational Activities
Not Applicables
Appendices
Dashboards & Reports
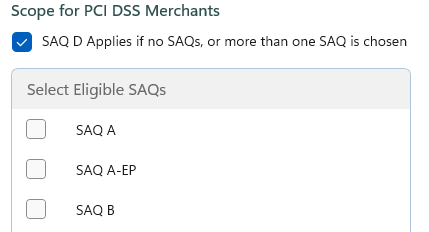
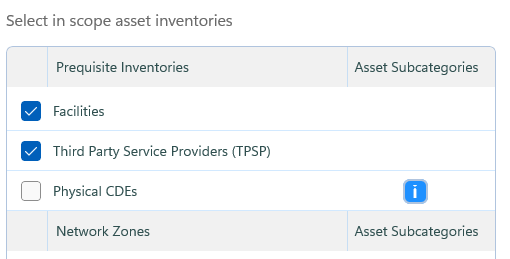
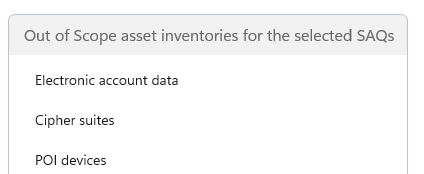
PCI Linx qualifies and confirms the correct scope for your organization, based on the inventory assets used across your Payment Card Environment.
This will link your in-scope assets, systems, processes and evidence and automatically assign them to the PCI DSS requirements.
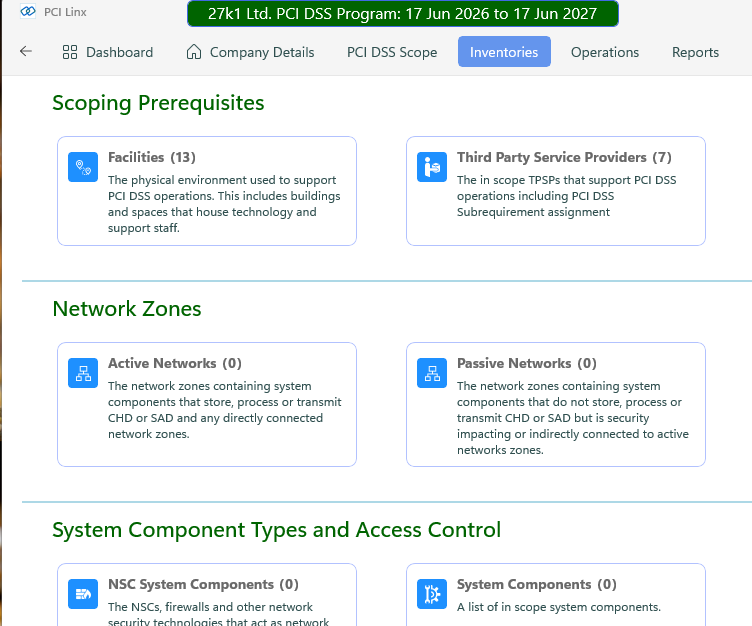
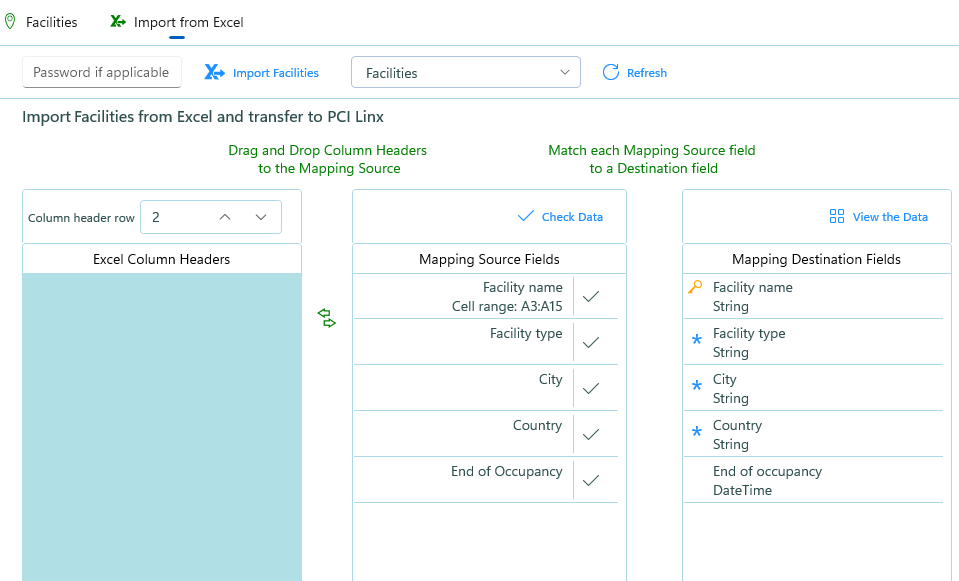
PCI Linx uses customized spreadsheets enabling you to easily upload, import and categorize the PCI assets from your organization’s asset registers.
This enables the accurate inventory management of hardware, software and cloud assets.
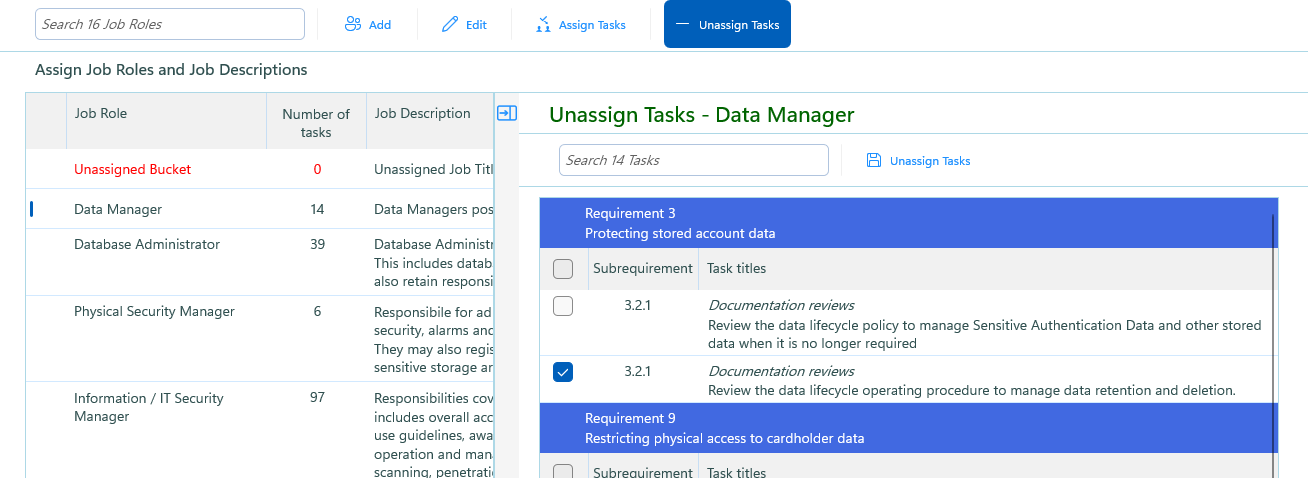
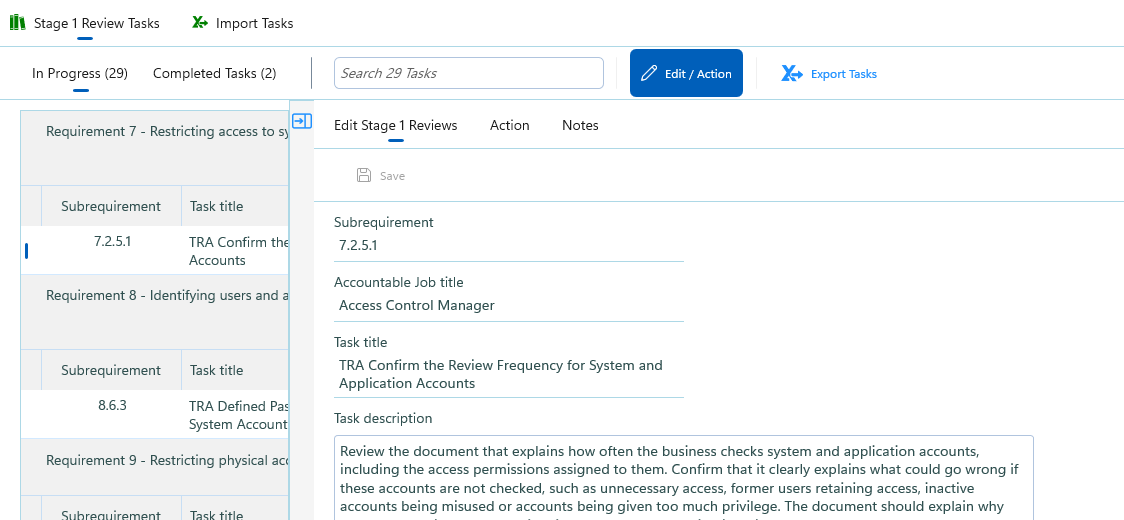
PCI Linx auto-allocates all PCI subrequirement tasks to their delegated recipient PCI DSS job roles.
Each task is written in clear, non‑technical language so that the IS team will readily understand and confidently action their allocated tasks.
Stage 1 Reviews - where your Payment Card Environment is prepared for assessment.
PCI DSS Documentation - where confirmation of the supporting records, policies, documents and evidence is linked into the system from your data repository using URL’s.
Examine Systems - where your PCI DSS security systems are checked and tested to ensure they have been properly implemented, maintained and operate as designed.
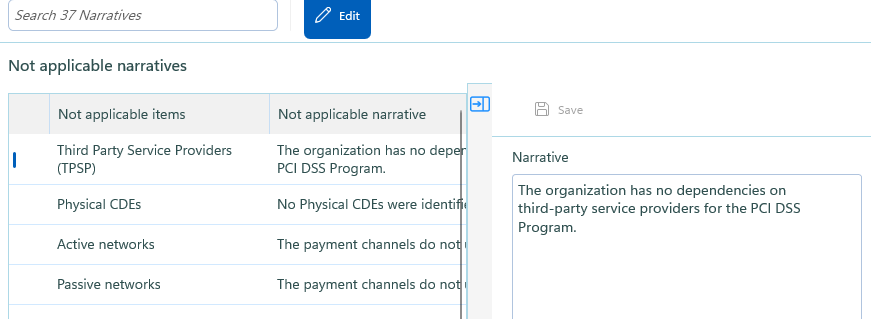
PCI Linx autopopulates the Not Applicables from a library of customizable narratives located in the Utilities section of the software.
On an exception basis and where a subrequirement has been deemed in-scope, PCI Linx facilitates a manual, Not Applicable submission.
Management reports provide Executive leadership with real time visibility of ongoing compliance activities, evidence tracking and task completion across all sites.
Progress reports provide the visibility of what is in scope, what needs to be done, who owns it and where the supporting artefacts live.
The reports give clarity to the organization’s overall PCI posture, providing assurance to the Merchant Executive Officers during the annual, PCI DSS sign‑off process.